
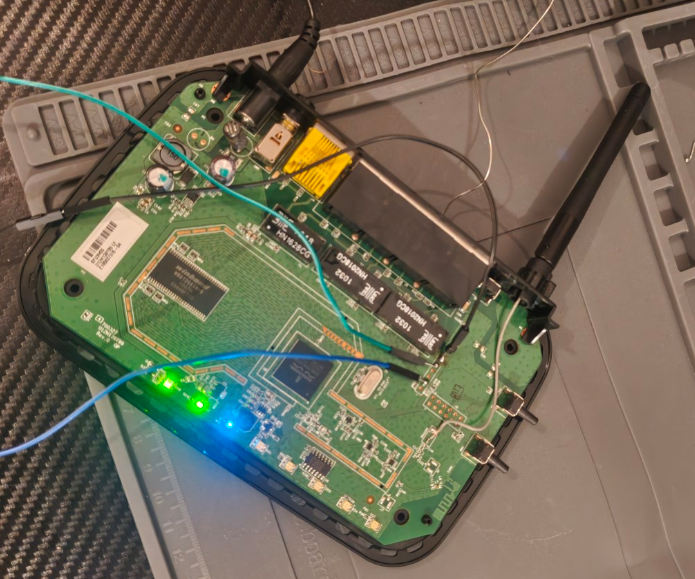
Hit Enter, Get Root: Unauthenticated RCE Chain on the NETGEAR WNR1000v3
A used NETGEAR router on the workbench: UART troubleshooting, firmware research, and lessons from investigating an end-of-life device.

A used NETGEAR router on the workbench: UART troubleshooting, firmware research, and lessons from investigating an end-of-life device.

A practical comparison of OSCP and CPTS from my own path into penetration testing: what each certification taught me, where they differ, and how they shaped real-world readiness.
Responsible endpoint-security research in an isolated Windows lab: how Microsoft Defender detects suspicious behavior, how to reason about controls, and how defenders can validate coverage.
A practical look at Active Directory trust relationships, why misconfigurations matter, and how defenders can reduce cross-domain attack paths.
ADCS is a critical identity component. This article explains why certificate-service misconfigurations matter and how to think about detection, hardening, and risk.
A high-level review of Sliver C2 concepts for authorized red team operations, with emphasis on lab scope, operational discipline, and defensive lessons.
Advanced DACL notes focused on misconfiguration impact, privilege paths, and how defenders can identify dangerous permissions.
An introduction to DACL security in Active Directory: permissions, abuse paths, and why access-control hygiene matters.
Kerberos security notes for Active Directory environments, covering ticket-based authentication concepts, common risks, and practical defensive awareness.